GDPR-Compliant Audio Processing: Practical Checklist
A practical GDPR checklist for teams handling voice recordings in browser or cloud-assisted workflows.
Browser Audio Workstation
Open the privacy-first browser audio workstation
Process audio in the browser and keep the original file off the Resodock server, which is useful for meetings, interviews, and private recordings.
Define data boundaries first
Identify which recordings are personal data, whether cross-border transfer exists, and where third-party processors are involved.
Then align processing mode, minimization policy, and verifiable deletion controls.
Back to the workstation
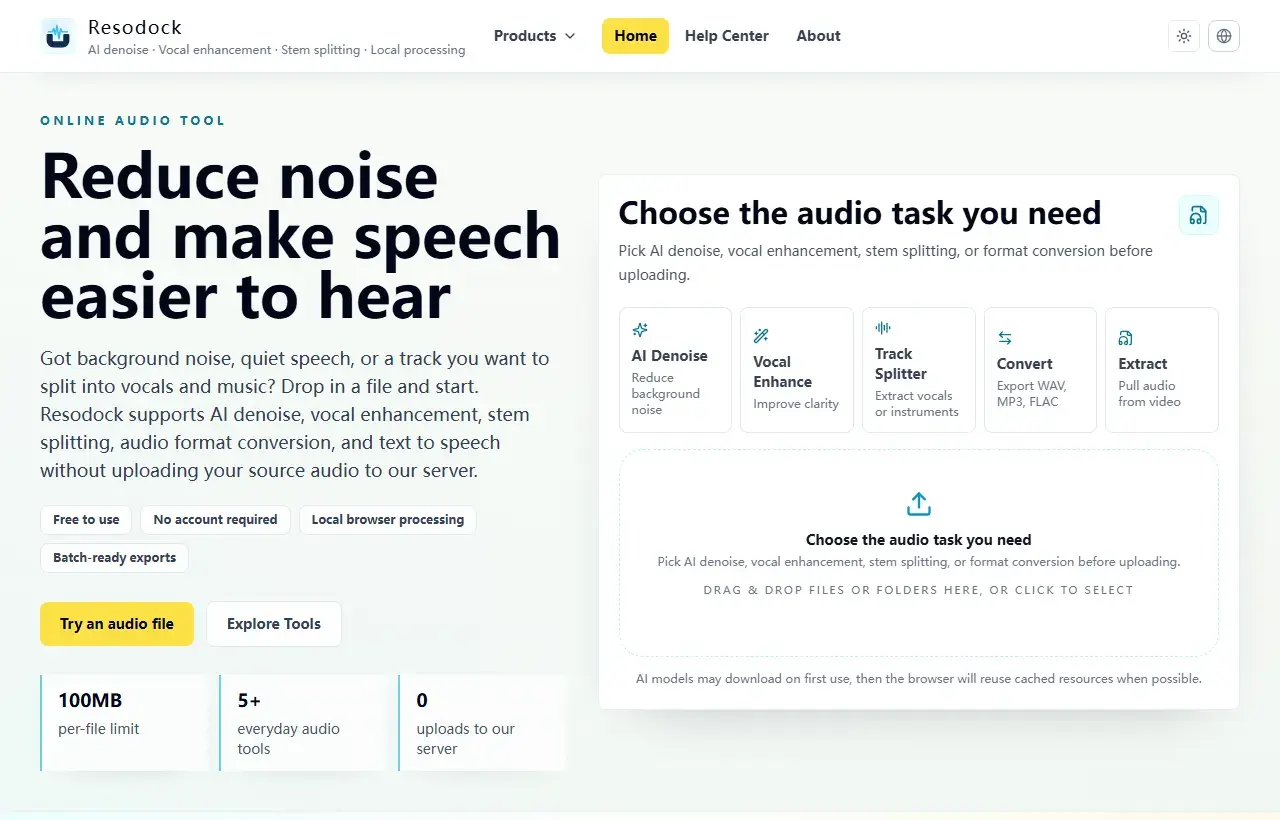
Choose a task, then upload the file
When an article mentions several workflows, the main workstation is the easiest place to start. Pick a task, upload the file, then preview and download the result.
- 1Open the Resodock workstation.
- 2Choose AI denoise, voice enhancement, stem separation, or format conversion.
- 3Upload the file and start processing.
- 4Preview the result and download it when ready.
Actionable compliance checklist
Implement access control, retention windows, deletion verification, incident response, and audit logging.
Documented workflow improves execution consistency and makes internal/external reviews easier.
Summary
For privacy-sensitive audio work, the key question is whether the raw file leaves your device and whether storage, deletion, and network behavior are clear.
For meetings, interviews, client material, or personal recordings, prefer browser-local processing and test the flow with a sample file first.
Related Articles
Privacy & Safety
Why Local Audio Processing Is Becoming The Default
For meetings, interviews, and client recordings, local processing is not just a feature claim; it is practical risk control.
Privacy & Safety
Are Online Audio Converters Safe? 6 Checks Before You Use One
The key issue is not just SSL. It is whether your raw audio is uploaded, retained, and reused.
Privacy & Safety
How To Choose Privacy-First Browser Audio Editors
You do not need a brand list first. You need a repeatable evaluation checklist.
FAQ
If audio is not uploaded, is GDPR compliance solved?
No. You still need proper access control, retention policy, deletion verification, and audit trail.
Do small teams need full compliance workflows?
They can scale by risk level, but core controls should still be present.